Meaning
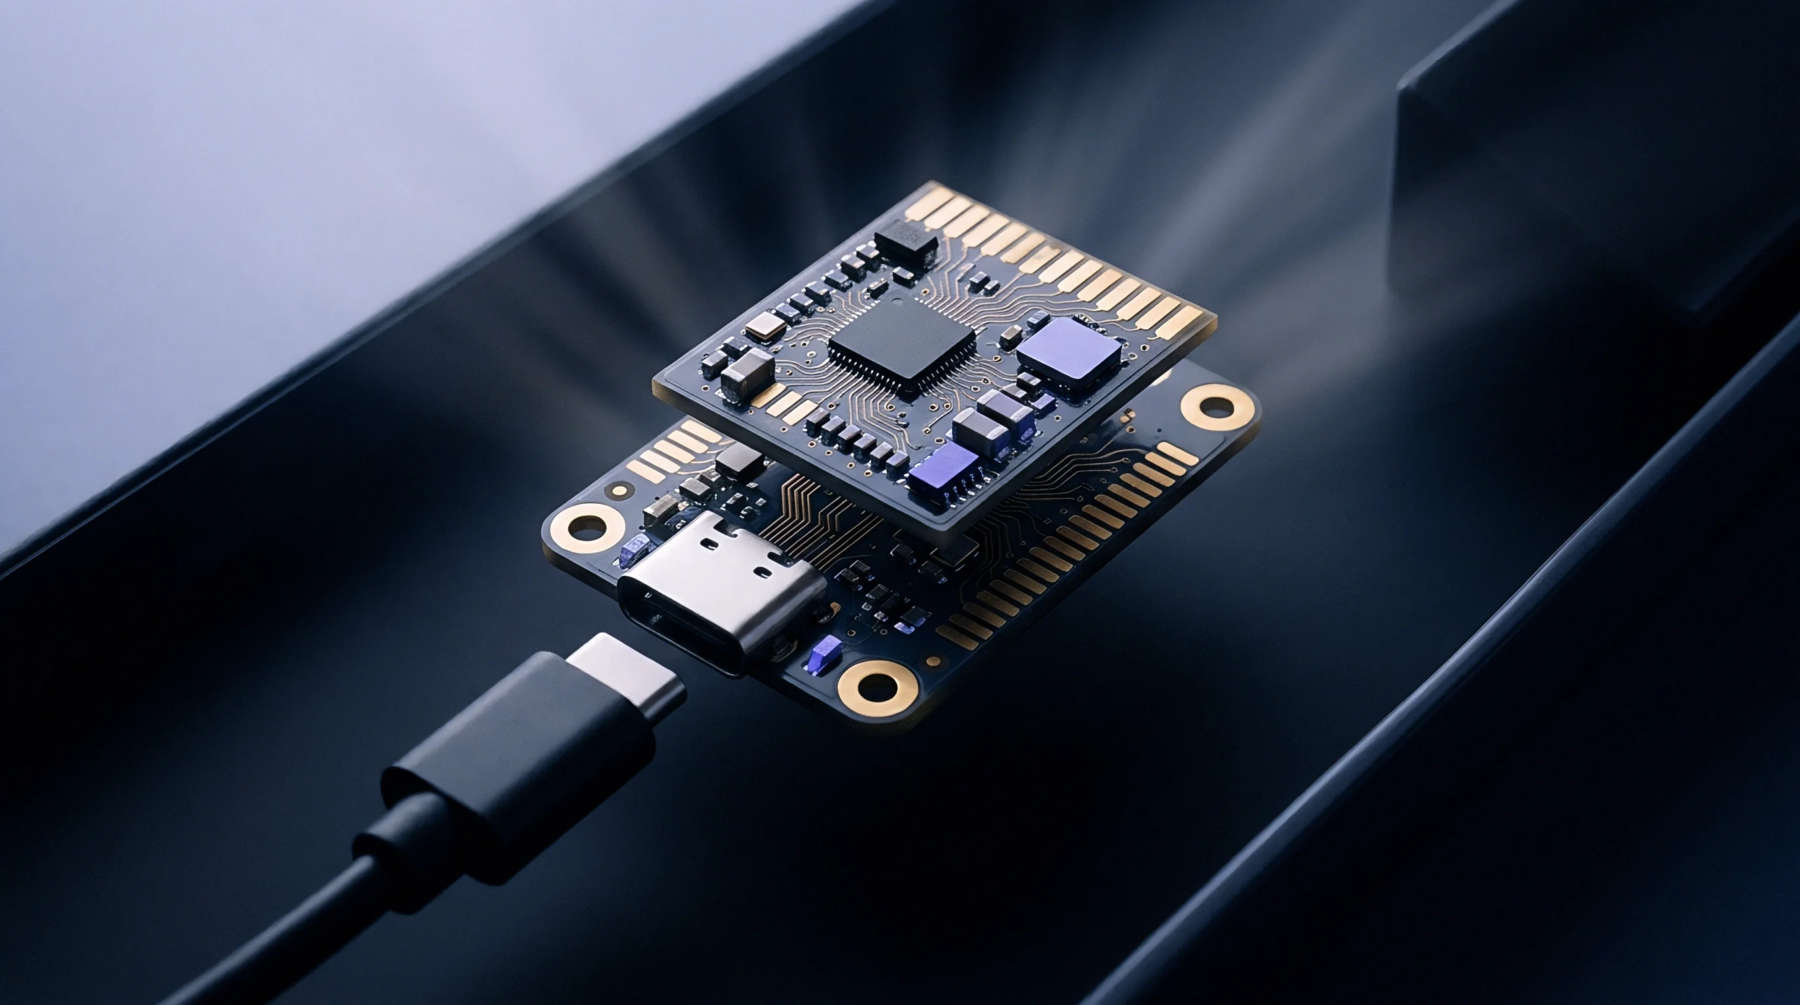
Software structure in an embedded microcontroller dictates how system start-up and secure firmware updates are executed. A multi-stage bootloader architecture establishes a chain of trust by isolating the initial boot code from the primary application image. This design ensures that the device can securely receive, authenticate, and unpack new firmware over wireless interfaces without risking a permanent brick state.
The boundary of this architecture sits between the raw hardware boot vector and the fully initialized operating system kernel.
Partition Strategy
Memory division on the flash chip allocates specific addresses for the factory-default image, the active application, and the incoming update package. In a dual-image design, the bootloader architecture relies on two equal memory slots to execute in-place switching, which allows the previous version to remain available if the new image fails to boot. This strategy dictates the physical sizing of the flash memory on the production circuit board.
If the system is constrained by a tight thermal or space budget, a single-slot architecture with compressed images is used instead, although this increases the time required to resume operation after an update. Choosing between these partitions influences the unit cost of the memory chip.
Verification Sequence
Cryptographic authentication of the newly downloaded firmware must occur before the execution control is handed over from the secure boot area. The bootloader architecture uses a hardware-accelerated public key verification step to inspect the digital signature of the binary image. If the signature is invalid, the system rejects the update and falls back to the golden image stored in read-only flash.
This check is completed during the initial power-up sequence, and the results are documented in the device register log for production testing.
Recovery Protocol
Failsafe execution ensures that a device remains accessible when a wireless transmission is interrupted midway through a flash write. If the application image becomes corrupted, the bootloader architecture initiates a fallback routine that boots the factory version from a protected sector. This routine prevents physical returns.